Hackers Used Chrome and Qualcomm GPU Flaws to Steal Data From Android and iOS Users
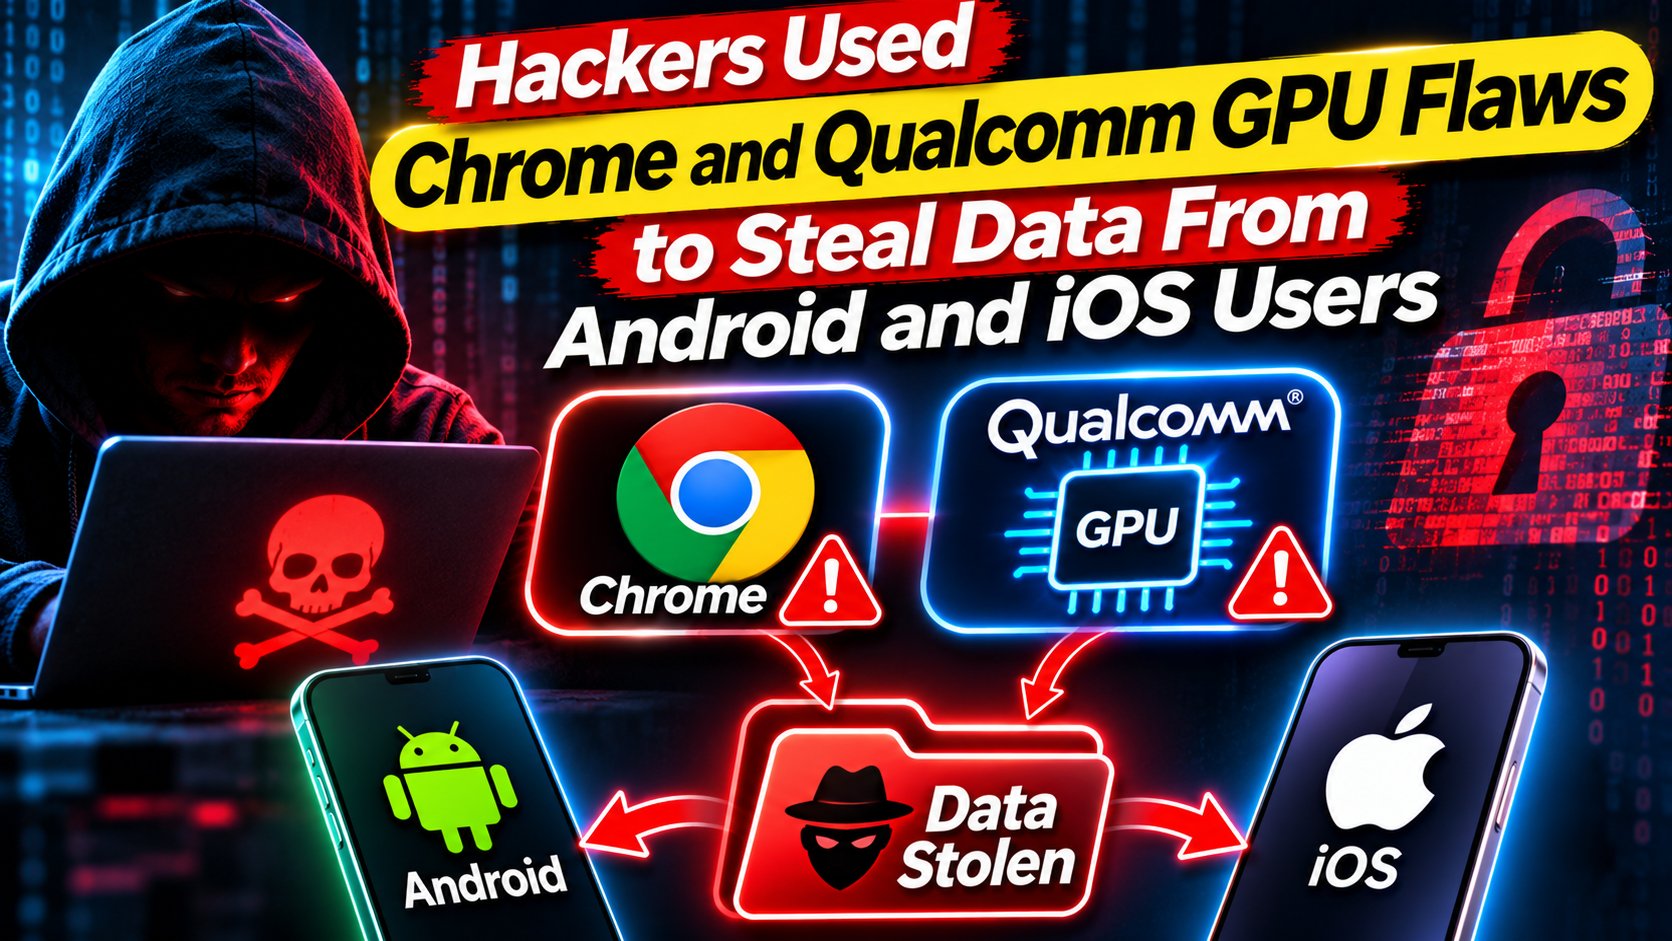
Hackers working for Russia’s APT29 group spent months breaking into Android and iOS phones through websites their victims trusted, according to new research from cybersecurity firm Sekoia. The attacks, which ran from June to September 2025, used flaws in Google Chrome and in Qualcomm’s Adreno graphics driver to steal data from people who simply visited a booby-trapped web page.
Sekoia’s Threat Detection and Research team, known as Sekoia TDR, published its findings on Wednesday, November 5. The report links the campaign to APT29 — also known as Midnight Blizzard or Cozy Bear — a group widely tied to Russia’s foreign intelligence service. The hackers’ goal, the researchers say, was to collect personal data from high-value targets.
What Sekoia found
The campaign used so-called watering-hole attacks: the hackers compromised real websites and planted malicious code on them, so that anyone who visited the site was attacked without needing to click anything suspicious. The sites were chosen to match the victims’ interests — a fake cloud service, a crypto trading platform, a government job board and a software download page were among the lures.
Sekoia first picked up the trail on August 19, 2025, when it spotted a crash in Google Chrome’s V8 JavaScript engine. Digging into that crash led the team to a full exploit chain — a sequence of flaws used one after another to break out of the browser and take control of the phone.
The payloads collected contacts, location data, lists of installed apps, SMS messages and device details, and sent them back to servers run by the hackers. In some cases the attackers also pushed extra code onto the device to keep gathering data over time.
The two flaws that opened the door
On Android, the chain started with a flaw in Chrome’s V8 engine, tracked as CVE-2025-2783, which let the attackers escape the browser’s sandbox — the safety box that is supposed to keep web code away from the rest of the phone. A second Chrome flaw, CVE-2025-2856, a type confusion bug in V8’s Mojo component, gave them a way to run code on the device.
The final step used a flaw in Qualcomm’s Adreno GPU driver, CVE-2025-24816, to gain the deeper access needed to read personal data. That driver flaw affects a long list of Snapdragon chips, including the 680 and 685, the 865 and 865+, the 888 and 888+, the 8 Gen 1, 2 and 3, the 8s Gen 3 and 4, and the 8 Elite Gen 5.
Google moved fast once the flaws were reported. CVE-2025-2783 was reported on March 20, 2025 and patched on March 25 in Chrome version 134.0.6998.88/89, while CVE-2025-2856 was reported on March 27 and fixed in April. The Adreno flaw was fixed in Qualcomm’s October 2025 security bulletin.
How the attacks reached victims
iOS users were not spared. The report says the campaign targeted both Android and iOS users, with the attackers using compromised websites to reach people on either platform. On Apple devices, the attacks worked through the browser too, which is why keeping Chrome and Safari up to date matters even on an iPhone.
The watering-hole approach is what makes this campaign hard to spot. Victims did not download a dodgy app or open a strange attachment — they visited a website that looked normal, and the attack ran in the background. That is also why the targets were chosen so carefully: the sites matched the work and interests of the people APT29 wanted to watch.
Who was targeted
Sekoia says the campaign focused on people in the United States, the United Kingdom, France and Spain, and that the victims were picked for their roles rather than at random. The researchers link the effort to APT29’s wider work, and note that Google’s own threat team has tied related activity to the same group.
Google said in October 2025 that the average time between a flaw being found and being used in real attacks had fallen to about 35 days, and that 71 flaws were used in live attacks during the first half of the year. The Chrome flaws in this campaign fit that pattern: both were reported by researchers, patched quickly, and still found their way into attacks within weeks.
How to protect your phone
The fix is simple, but it only works if you install it. Update Chrome to version 141.0.7390.122 on Android, or 141.0.7390.119 on iOS, and install the latest Android security patch, which carries the Adreno driver fix. Turn on automatic updates for your browser and your phone’s system software so you do not have to remember.
Beyond updates, the usual habits still help: be wary of links in messages and emails, even when they look like they come from someone you know, and avoid downloading apps from outside the official stores. If you use a phone for work that involves sensitive information, treat a browser update prompt as urgent rather than something to put off. Even the biggest tech companies are rethinking their security posture, and Apple’s engineers are working under new limits on the AI tools they use.
Read the full findings from Sekoia, the latest Chrome releases on Google’s Chrome Releases blog, and the report on Gadgets 360.